For the complete documentation index, see llms.txt. Markdown versions of all docs pages are available by appending .md to any docs URL.
Export logs over OTLP
Export agentgateway access logs as OTLP LogRecord objects to an OpenTelemetry Collector or any compatible backend.
Log export happens in addition to stdout output, so you can send logs to a collector without losing local visibility.
This guide walks through setting up an OpenTelemetry Collector to receive access logs from agentgateway.
The way you set up the collector depends on how you installed agentgateway.
Binary and Docker installations
Run the OTel Collector as a Docker container on the same host as agentgateway.
Create an
otel-collector-config.yamlfile that defines an OTLP receiver and a logs pipeline.cat > otel-collector-config.yaml << 'EOF' receivers: otlp: protocols: grpc: endpoint: 0.0.0.0:4317 processors: batch: exporters: debug: verbosity: detailed service: pipelines: logs: receivers: [otlp] processors: [batch] exporters: [debug] EOFReplace the
debugexporter with the exporter for your logging backend (for example, Loki, Elasticsearch, or an OTLP-compatible storage system).Start the OTel Collector container and mount your config file.
docker run -d --name otel-collector \
  -p 4317:4317 \
  -v $(pwd)/otel-collector-config.yaml:/etc/otelcol/config.yaml \
  otel/opentelemetry-collector:latest
Configure agentgateway to send access logs to the collector. You can make this change in the UI or in your configuration file.
Whether the UI can save depends on your storage mode. For more information, see Save changes from the UI.
Open the Settings > Observability page, such as http://localhost:15000/ui/settings/observability, and click the Access logs card.
In the OTLP export section, select Export logs over OTLP.
Keep
localhost:4317for the Collector host and gRPC for the Protocol.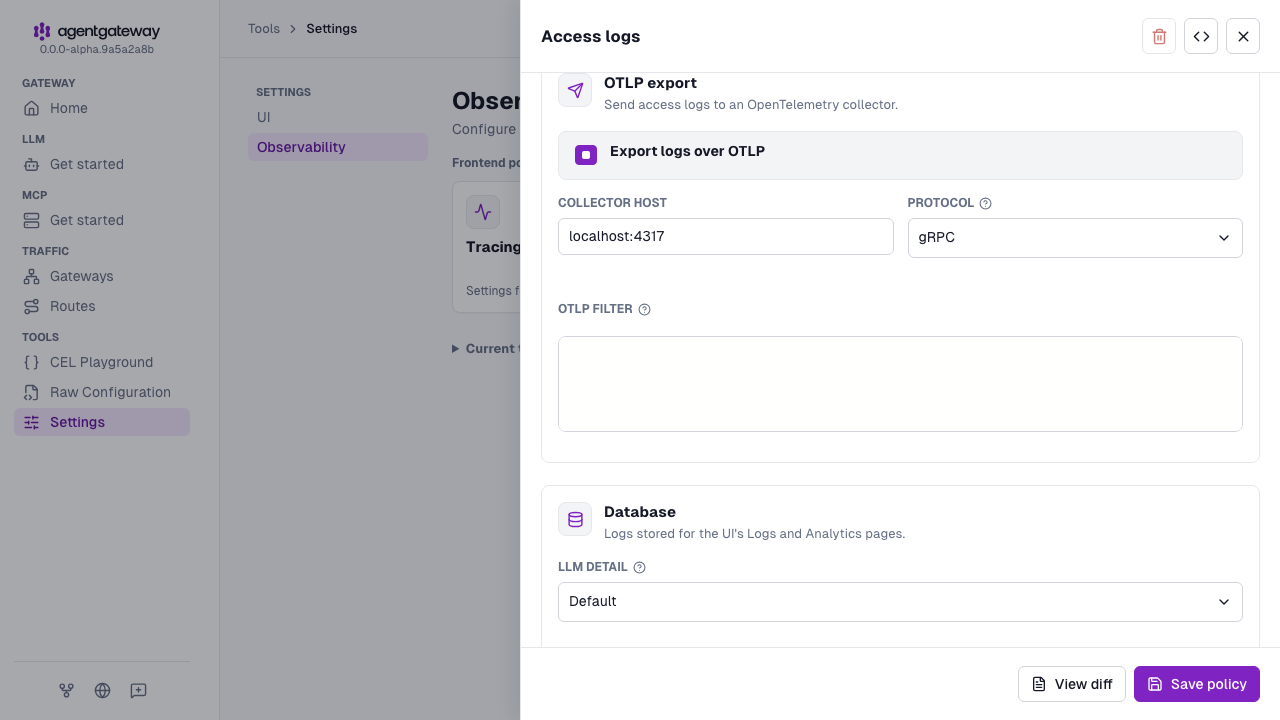
Click Save policy. The UI saves the
frontendPolicies.accessLog.otlpsection in your configuration.
Send a request through agentgateway, then check the collector output to verify that log records are arriving.
docker logs otel-collectorEach proxied request appears as a
LogRecordentry in the collector output. Look for a block that starts withLogRecord #and includes attributes such asgateway,http.request.method,url.path, andhttp.response.status_code. The HTTP attributes use the OpenTelemetry semantic convention names. The records belong to theagentgateway.accessinstrumentation scope, which the collector prints in theInstrumentationScopeline of theScopeLogsblock that contains the record.When you are done, remove the OTel Collector container.
docker rm -f otel-collector
Helm installations
Deploy the OTel Collector into your cluster by using the OpenTelemetry Helm chart and point agentgateway at its service.
Add the OpenTelemetry Helm repository.
helm repo add open-telemetry https://open-telemetry.github.io/opentelemetry-helm-charts helm repo updateCreate a
values.yamlfile that defines the collector pipeline.mode: deployment config: receivers: otlp: protocols: grpc: endpoint: 0.0.0.0:4317 processors: batch: exporters: debug: verbosity: detailed service: pipelines: logs: receivers: [otlp] processors: [batch] exporters: [debug]Replace the
debugexporter with the exporter for your logging backend.Install the OTel Collector chart.
helm install otel-collector open-telemetry/opentelemetry-collector \ -n monitoring --create-namespace \ -f values.yamlVerify that the collector pod is running.
kubectl get pods -n monitoringUpdate your agentgateway
values.yamlto send access logs to the collector service. The chart takes the agentgateway configuration under the top-levelconfigfield.config: frontendPolicies: accessLog: otlp: host: otel-collector.monitoring.svc.cluster.local:4317Apply the change with a Helm upgrade.
helm upgrade -i agentgateway-standalone \ oci://cr.agentgateway.dev/charts/agentgateway-standalone \ --namespace agentgateway-system \ --version 0.0.0-latest-dev \ --reuse-values \ -f values.yamlSend a request through agentgateway, then check the collector logs to verify that log records are arriving.
kubectl logs -n monitoring deployment/otel-collectorEach proxied request appears as a
LogRecordentry. Look for a block that starts withLogRecord #and includes attributes such asgateway,http.request.method,url.path, andhttp.response.status_code. The HTTP attributes use the OpenTelemetry semantic convention names. The records belong to theagentgateway.accessinstrumentation scope, which the collector prints in theInstrumentationScopeline of theScopeLogsblock that contains the record.When you are done, remove the OTel Collector and the monitoring namespace.
helm uninstall otel-collector -n monitoring kubectl delete namespace monitoring
Other configurations
Review other common configurations when exporting access logs to an OTLP-compatible backend.
Filter logs before export
You can filter which access logs are exported to your OTLP backend by setting the accessLog.otlp.filter field. When otlp.filter is not set, the top-level filter (frontendPolicies.accessLog.filter) is used as a fallback for OTLP export as well. When otlp.filter is set, it takes precedence over the top-level filter for OTLP export only, so you can send a different subset of logs to your OTLP backend than to stdout and the database.
The following example sends only error responses to the OTLP collector while logging all requests to stdout.
Open the Settings > Observability page, and click the Access logs card.
In the OTLP export section, select Export logs over OTLP, and keep
localhost:4317for the Collector host.Enter
response.code >= 400in the OTLP filter field. To set the top-level filter instead, use the Filter field in the Log fields section.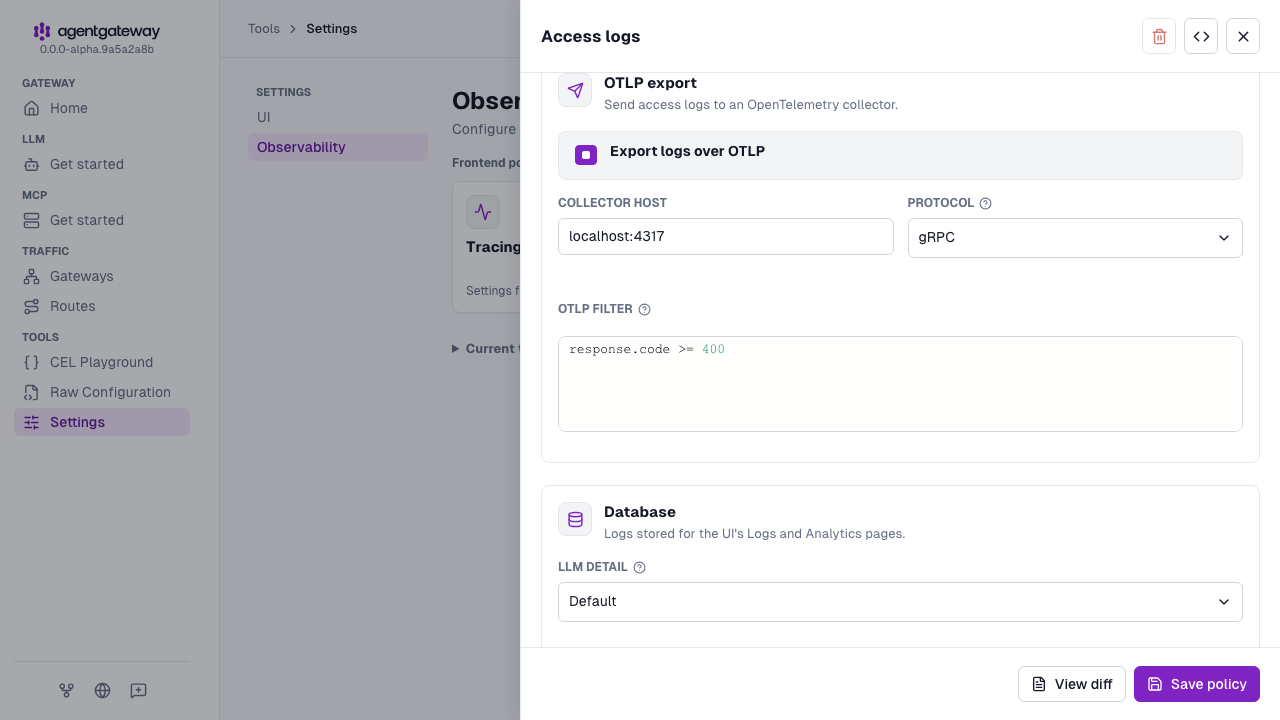
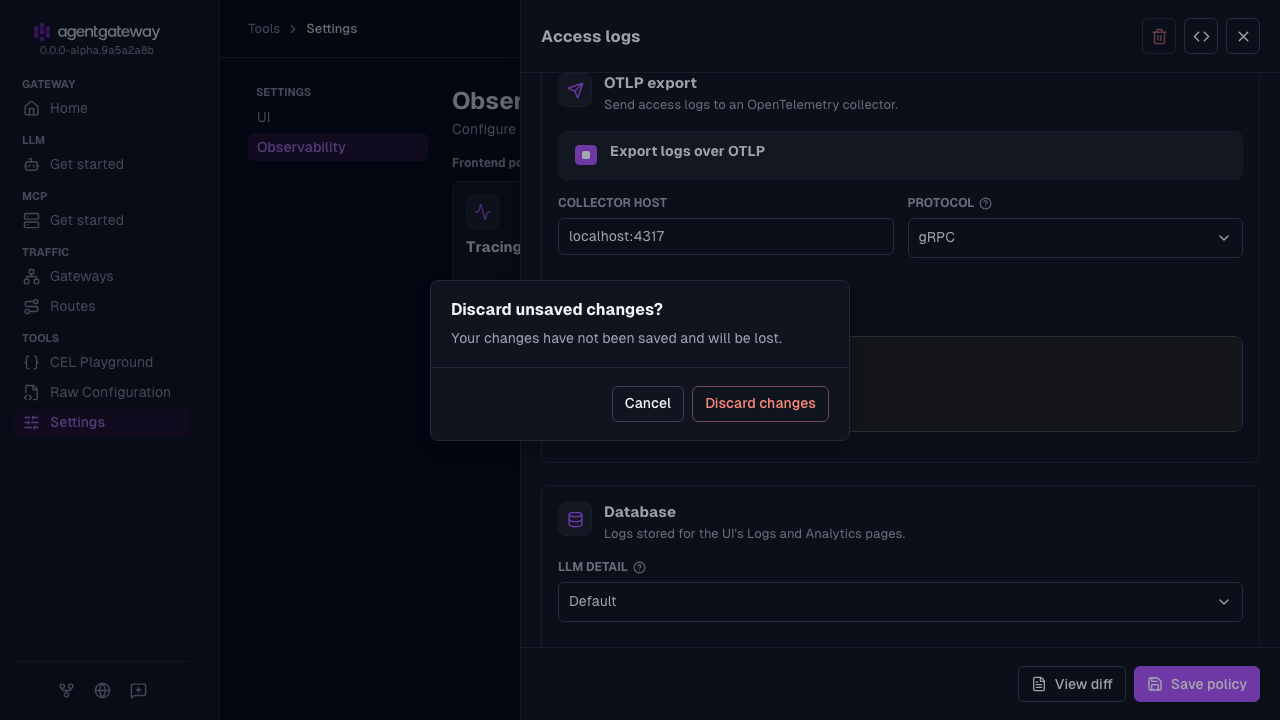
Click Save policy.
The following example logs only error responses to stdout, the database, and the OTLP collector. Because no otlp.filter is set, the top-level filter applies to all three backends.
# yaml-language-server: $schema=https://agentgateway.dev/schema/config
frontendPolicies:
accessLog:
filter: 'response.code >= 400'
otlp:
host: localhost:4317The following example logs only error responses to stdout and the database, but sends all requests to the OTLP collector. To override the top-level filter for OTLP, set otlp.filter explicitly.
# yaml-language-server: $schema=https://agentgateway.dev/schema/config
frontendPolicies:
accessLog:
filter: 'response.code >= 400'
otlp:
host: localhost:4317
filter: 'true'Customize exported fields
You can add or remove fields to the log entry that you export to the OTLP endpoint. The following example adds a trace_id field from the x-trace-id request header and removes the server.address field.
The remove list matches the attribute names in the OTLP record, which are the OpenTelemetry semantic convention names, such as server.address, url.path, and http.response.status_code. The stdout log keeps the http.host, http.path, and http.status names, and the OTLP fields setting does not change it. A name that does not appear in the OTLP record, such as http.host, removes nothing.
The UI has no field for otlp.fields, so set it in your configuration file.
# yaml-language-server: $schema=https://agentgateway.dev/schema/config
frontendPolicies:
  accessLog:
    otlp:
      host: localhost:4317
fields:
add:
trace_id: 'request.headers["x-trace-id"]'
remove:
- server.address